Cloud security and governance
Assessment of your AWS, Azure and GCP environments under the shared responsibility model. Maturity scoring, target operating model (TOM) and a prioritized roadmap.
Your security is our priority
obKoni helps banks, public bodies and growing companies assess cyber risk, design their access architecture and deliver critical IT projects. You work directly with senior consultants.
Featured
Cybersecurity
AWS, Azure and GCP assessments aligned with NIST, CIS and ISO 27002, with a roadmap prioritized by risk.
Learn more
Identity and access
Okta and Entra ID identity platforms, SAML and OIDC federation, built for millions of users.
Learn more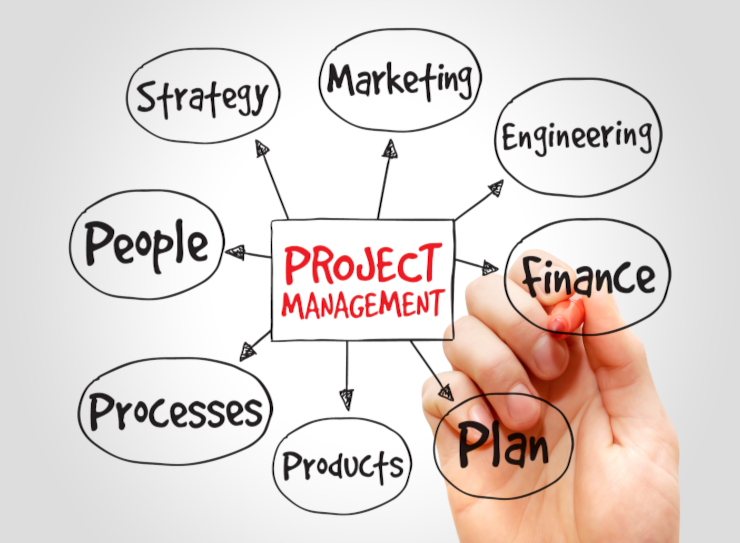
IT project management
Planning, cutovers, governance and budget tracking, in Agile or waterfall.
Learn moreExpertise
Every mandate ends with a concrete deliverable: an assessment report, a target architecture, a roadmap or a delivered project.
Assessment of your AWS, Azure and GCP environments under the shared responsibility model. Maturity scoring, target operating model (TOM) and a prioritized roadmap.
Web and API penetration testing, threat modelling and attack trees. Risk-rated reports with remediation your teams can act on.
Design and rollout of workforce and customer identity platforms: federation, strong authentication, provisioning. Experience with journeys serving over a million users.
SIEM and SOAR architecture, security data pipelines and forensic environments on AWS. Detect earlier, respond faster.
Risk assessment specific to artificial intelligence systems: data, models, integrations and governance, aligned with your compliance obligations.
Design and development of web applications and APIs, containerization and Kubernetes orchestration, CI/CD pipelines with security built in from the start.
Leading migrations, infrastructure modernization and project portfolios: schedules, budgets, RAID logs, cutovers and governance, in Agile or waterfall.
Industries
Mandates delivered by our consultants, directly or through partners.
Banks and insurers: cloud security, IAM and regulatory compliance.
Ministries and agencies: Agile IT projects and governance.
National-scale infrastructure migration and modernization.
Project portfolios, budget tracking and dashboards.
Application security, SOC 2 and ISO for software vendors.
Structuring operations and performance management tools.
Organizations that trusted us.
Approach
Business goals, scope, regulatory constraints and stakeholders.
Gap analysis in the field, grounded in recognized frameworks.
Target architecture and an action plan prioritized by risk and cost.
Hands-on support for your teams through go-live and handover.
Frameworks we apply
Profiles
We build each team from these profiles, from strategic advice to technical delivery.
Expert · 20+ years in IT
Maturity assessments, cloud architectures and AI systems, target operating models and roadmaps for IT and security leadership.
Senior · AI governance and security
AI governance, security of AI systems, AI for defenders and AI in the software development lifecycle (SDLC).
Senior · large-scale platforms
Design and rollout of workforce and customer identity platforms, federation and provisioning, on journeys serving over a million users.
Senior · Web and API
Penetration testing, threat modelling and DevSecOps support, with risk-rated reports.
Senior · cloud-native
Design and development of web applications and APIs, containerization and deployment on Kubernetes, secure CI/CD pipelines.
Senior · 15+ years
Infrastructure migrations and modernization, cutovers, RAID logs, governance and budget tracking, in Agile or waterfall.
Senior · Europe
Leading information systems projects for clients in France, from study to go-live.
Talk it through with a senior consultant. First conversation, no commitment.
Contact
Tell us about your context in a few lines. We reply within two business days.
Sainte-Marthe-sur-le-Lac (Greater Montreal), Québec, Canada